Skip to content
No results
  • Contents
    • Docker
    • Kubernetes
    • Network Automation
    • Cloud Platforms
      • OCI
        • IAM
        • OCI Networking
      • Professional Cloud Architect
      • Cloud Network Engineer
      • Google Cloud Network Engineer Practice Tests
      • OCI for GCP Architects
    • GIT & Version Control
    • Terraform Articles
      • Terraform-AWS-Labs
      • Terraform-GCP-Labs
      • Terraform Practice Lab
      • terraform-practice-tests
    • Multicast
    • ACI
  • About Me
ethernetdude
  • OCI, IAM

Article 12 – Tag-Based Access Control (TBAC) & Attribute-Based Access Control (ABAC)

1. Introduction to Dynamic Metadata Governance As enterprise cloud footprints grow to encompass thousands of compute VMs, storage buckets, and subnets across dozens of compartments, managing static compartment-based IAM policies becomes an operational bottleneck. Oracle Cloud Infrastructure (OCI) solves this…

  • OCI, IAM

Article 13 – Security Zones & Security Guardrails: Enforcing Inviolable Policy Constraints

1. Introduction to Kernel-Level Security Guardrails Standard IAM policies define who is allowed to perform actions on cloud resources. However, in high-security production environments, organizations need inviolable guardrails—kernel-level rules that prevent non-compliant configurations (such as creating a public storage bucket…

  • OCI, IAM

Article 14 – IAM Audit Logging, Cloud Guard, and Security Posture Monitoring

1. Introduction to Posture Monitoring and Auditability In enterprise cloud governance, tracking who performed what action, on which resource, and from which IP address is a critical requirement for security compliance and incident investigation. Oracle Cloud Infrastructure (OCI) delivers native,…

  • OCI, IAM

Article 15 – OCI Console Navigation & Administrative Workflows: Mastering the IAM Web Interface

1. Introduction to the OCI Console IAM Interface The Oracle Cloud Infrastructure (OCI) Web Console provides a unified graphical interface for managing tenancy administration, identity directories, policy documents, and governance guardrails. While command-line tools (OCI CLI) and SDKs are used…

  • OCI, IAM

Article 16 – API Keys, Auth Tokens, OAuth2 Clients, and Service User Authentication

1. Introduction to Programmatic Authentication While human users log into the OCI Web Console using a username, password, and MFA factor, automated applications, scripts, CLI tools, and microservices require programmatic authentication mechanisms. Oracle Cloud Infrastructure (OCI) provides three primary non-interactive…

  • OCI, IAM

Article 18 – IAM Troubleshooting & Diagnostic Mechanics: Resolving Production Access Failures

1. Introduction to IAM Diagnostic Engineering Even well-designed Oracle Cloud Infrastructure (OCI) identity architectures can encounter access failures due to policy syntax errors, missing verbs, network source IP drift, or dynamic group matching rule typos. When an OCI SDK, CLI…

  • OCI, IAM

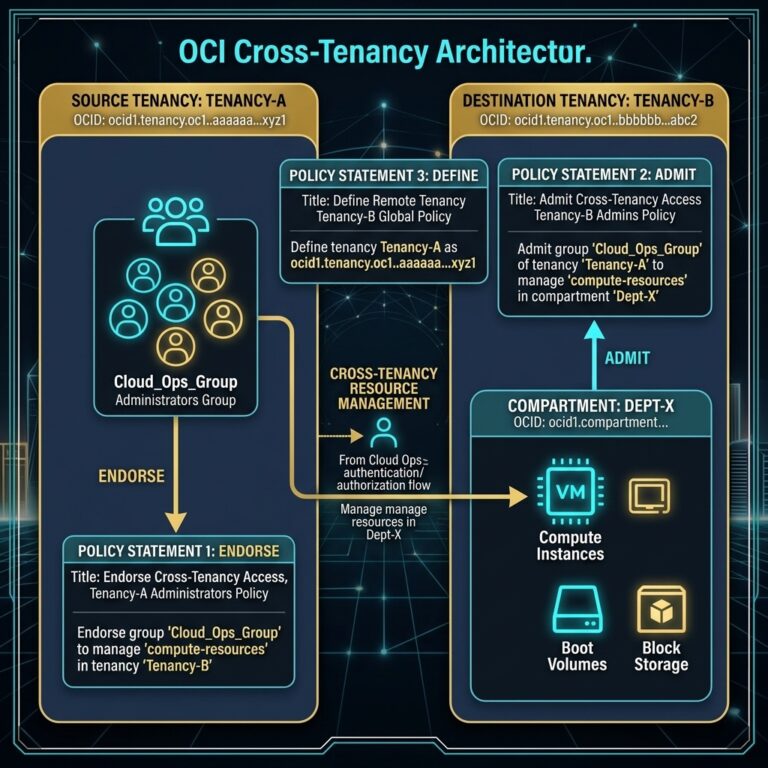
Article 17 – OCI IAM Cross-Tenancy Access & Compartment Delegation Architectures

1. Introduction to Multi-Tenancy Governance In enterprise cloud operations, organizations often maintain multiple distinct OCI Tenancies—such as separate tenancies for different subsidiaries, independent business units, or Managed Service Provider (MSP) partner access. By default, OCI tenancies are completely isolated cryptographic…

  • OCI, IAM

Article 19 – OCI IAM Comprehensive Knowledge Assessment and Scenario Guide

Instructions This standalone assessment is designed to test your knowledge of Oracle Cloud Infrastructure (OCI) Identity and Access Management (IAM) across all 18 topics in the series. Work through the scenario questions in Section 1 first without scrolling down. Once…

  • OCI for GCP Architects

Article 11 – OCI Security and Management: Governance, Observability, and Resource Manager

The Multi-Tool Security Headache In many cloud environments, operational governance and system observability are fragmented across multiple disconnected services. If you want to secure an environment in Google Cloud, you configure Organization Policies at the resource folder level, monitor configurations…

  • OCI for GCP Architects

Article 10 – OCI Load Balancing: Traffic Distribution and DNS steering

The Global vs. Regional Proxy Trade-Off In Google Cloud, Cloud Load Balancing is a global, software-defined service. When you deploy a Global External HTTP(S) Load Balancer, it utilizes Google’s global Edge network. Traffic from a client enters the closest Edge…

Prev
1 2 3 4 5 6 7 … 34
Next

[email protected]

Establish a Persistent Connection

Like the content ? Get notified when I post something new. I promise not to spam your Email.

Name
Enter your email address